The Lights Stay On, the Records Don't: When Ransomware Reaches Your Hometown
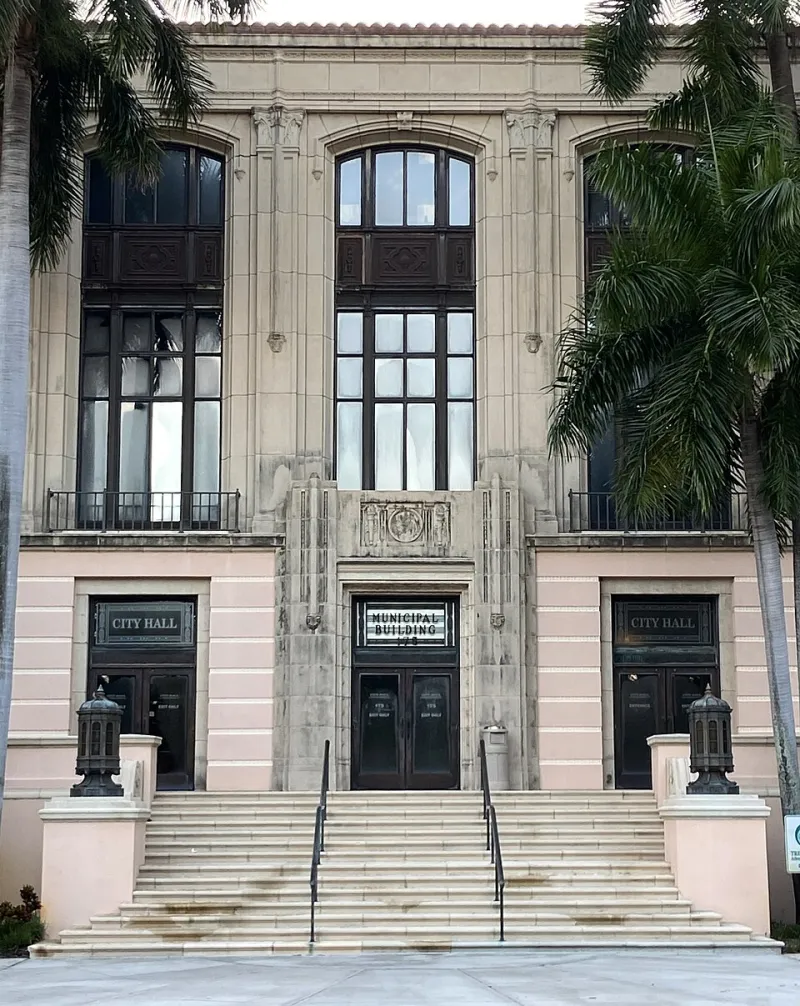
Photo: Myotus, CC BY 4.0, via Wikimedia Commons
A Different Kind of Breach Story
When a retailer is breached, the story has a familiar shape: a disclosure, a credit monitoring offer, a slow drift back to normal. When a city is breached, the story is messier. The affected organization is not a single company but a patchwork of departments — utilities billing, property records, permits, courts, public health, payroll — each holding data that residents never chose to hand over to a single entity.
That is what makes municipal ransomware a distinct problem. The victim is not a customer base; it is a population. And the people whose records sit inside those systems usually learn about it last.
Why City Hall Is an Attractive Target
The incentives line up badly. Local governments run twenty-four-hour services, cannot afford extended downtime, and often operate on thin IT budgets with legacy systems that were never designed for a networked world. Consolidation has helped in some places and created concentration risk in others. A single county government may now administer systems for dozens of agencies that were once independent.
The historical record is instructive. Atlanta's 2018 incident forced staff onto paper for weeks. Baltimore's 2019 attack cost the city an estimated eighteen million dollars. Dallas and Fulton County both dealt with significant intrusions in 2023 and 2024. These are not anomalies; they are a pattern with a recognizable shape.
How a Municipal Breach Typically Unfolds
The entry point is rarely exotic. Public-sector incident reviews repeatedly point to the same handful of causes: a stolen credential used to log into a remote-access portal, an unpatched internet-facing server, a phishing email opened by an employee with more access than the job required. Once inside, attackers spend days or weeks mapping the network before deploying anything, which is why the gap between intrusion and disruption can be long.
When encryption finally lands, the visible effects are mundane and disorienting at the same time. Online bill payment stops working. Permit applications go offline. Email bounces. Staff at the counter cannot pull up a record that existed the day before. Emergency services are usually prioritized and protected, but not always unaffected.
What Residents Should Expect — and When
Two separate clocks start running.
The first is operational: the city will announce service disruptions quickly, often within hours, because the outage is impossible to hide. The second is legal. Notification obligations vary by state, and public agencies frequently need forensic work to determine whose data was actually exposed. That gap between disruption and disclosure can run into months, and residents should not read silence as a clean bill of health.
What residents should look for is specificity. A notice that says the city experienced a cybersecurity incident is close to meaningless. A notice that identifies the categories of data involved, the departments affected, and whether records such as Social Security numbers, driver's license numbers, or health information were present is what actually allows a person to act.
The Downstream Tax
The secondary harms are the ones that linger. Property and tax records interrupted by an outage can delay closings and title searches. Utility billing systems that go offline often produce estimated charges and adjustment notices that take months to reconcile. Small contractors who depend on municipal permit portals lose work when those portals disappear for a week.
There is also a quieter concern: a compromised municipal network may hold data that residents did not know was collected — call recordings, inspection notes, benefits case files, and internal correspondence. Each of these expands the surface for identity fraud and for the kind of targeted deception that follows publicized breaches.
Questions Worth Asking Your Local Officials
Residents do not need to be security professionals to ask useful questions. The following are reasonable, and public records law in most states supports them.
- What is our cyber insurance position, and does it cover recovery or only response? Insurers increasingly require basic controls as a condition of coverage, which makes this a proxy for overall posture.
- Do we have a written incident response plan, and when was it last tested? A plan that has never been exercised is a document, not a capability.
- Is multi-factor authentication required for remote access to city systems? This single control blocks a large share of intrusions.
- How long do we retain sensitive data we no longer need? Retention is a security control. Every year a record sits on a server is another year it can be stolen.
- Will the city notify affected residents directly, or only through a website posting? Direct notice reaches the people who need it; a web page reaches the people who happen to look.
- Who is accountable for the annual IT security budget, and has it changed since the last incident?
A Realistic Standard
No city can promise it will never be breached, and officials who make that promise should be treated with skepticism. What a well-run municipality can offer is preparation: tested backups, segmented networks, mandatory second factors, and a communications plan that reaches residents before rumor does.
For residents, the practical takeaway is to assume that some record about you lives in a county system, to freeze your credit before you need to, and to treat any unexpected message citing a local government outage as suspect until verified through an official channel. The lights staying on is not the same as the records being safe.